SFTPPlus Release 3.32.0
We are pleased to announce the latest release of SFTPPlus version 3.32.0.
Continue reading


This is a subset of our news articles, filtered by tag.
We are pleased to announce the latest release of SFTPPlus version 3.32.0.
Details of attacks on DES (Data Encryption Standard) and Triple DES, Birthday attacks on 64-bit block ciphers were released with the CVE ID of CVE-2016-2183. Read more about the CVE details here.
SFTPPlus is not affected by Meltdown and Spectre. SFTPPlus secure file transfers does not allow any arbitrary application code execution.
We are pleased to announce the latest release of SFTPPlus version 3.31.0.
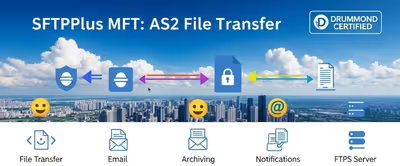
In order to implement a secure managed file transfer system, you will need a good understanding of the supported services and protocols involved.
In order to have a fully established file transfer and sharing system, you need to implement integration at all the other layers including the OS. SFTPPlus can be integrated with external tools and third parties in order to help establish these integration requirements.
We are pleased to announce the latest release of SFTPPlus version 3.28.0.
We are pleased to announce the latest release of SFTPPlus version 3.27.0.
We are pleased to announce the latest release of SFTPPlus, version 3.6.0.
SFTPPlus Server versions 1.6 and newer are not vulnerable to the DROWN attack.